


Seamless Multifactor Authentication
The most comprehensive list of authentication modalities in the industry.
How can OmniDefend’s MFA Secure Your Organization?


How OmniDefend MFA Works
OmniDefend MFA adds a security layer to your applications, devices, and networks by enforcing two or more verification factors at login. These factors include:
- Something you know (password, PIN)
- Something you have (smartphone, hardware token, smart card)
- Something you are (biometric information such as fingerprint, face, or voice)
You can deploy OmniDefend with your existing setup by utilizing API connectors, LDAP/AD integration, or third-party identity providers. No matter whether users are connecting to cloud apps, remote desktops, VPNs, or legacy systems, OmniDefend provides strong authentication across all access points.
Biometric Devices


Smart Cards
One-Time Passwords


Mobile Authenticator
FIDO2 WebAuthN
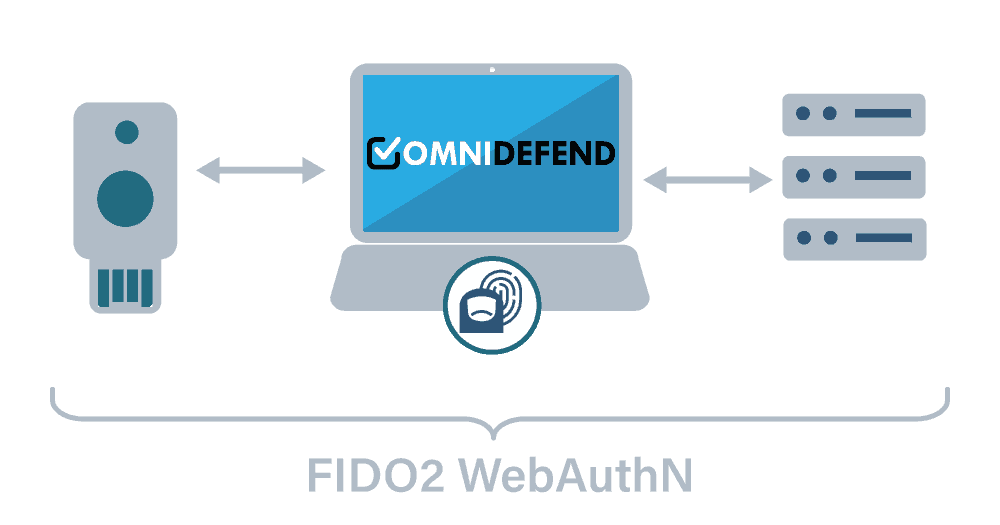

Authentication Flow Example:
- User enters username and password
- System evaluates risk via policy engine (location, device, IP, etc.)
- Based on risk score, the user is prompted for a second factor (e.g., mobile push, fingerprint, or OTP)
- Access is granted or denied
Get Started with OmniDefend MFA
Why Choose OmniDefend MFA?
Whereas solutions such as Duo and Okta are good, OmniDefend elevates MFA further by providing high-end biometric identification (1:N), on-premises deployment, and legacy infrastructure support without any compromise on contemporary cloud-native compatibility.
- FIDO2, WebAuthn, and OATH-compliant
- High-end biometric modalities: fingerprint, face, voice, palm vein
- Cloud, hybrid, or on-premise deployment
- 1:N biometric matching for large-scale identity searches
- Smart card & badge support with match-on-card technology
- Real-time access policies and threat detection

Frequently Asked Questions
OmniDefend MFA is a cloud-based offering that allows organizations to easily and rapidly incorporate multiple layers of authentication into their current applications, networks, and other systems. It rides on existing forms of authentication like passwords, hardware tokens, and biometric data, and adds a further layer of protection by imposing an additional factor, i.e., one-time passcode or biometric scan.
OmniDefend MFA facilitates many types of authentication methods, such as passwords, hardware tokens, biometrics, one-time passcodes, etc.
No. OmniDefend MFA is a cloud-based solution, so no additional hardware or software is required. OmniDefend is equipped to run on-premise as well.
Yes. OmniDefend MFA is designed to be easy to use, and requires minimal setup and configuration.
Yes. OmniDefend MFA is built on a secure, reliable cloud infrastructure that is designed to protect against unauthorized access and protect data from being compromised.
Pricing for OmniDefend MFA depends on the number of users, so please contact us for more information.
Yes. OmniDefend MFA offers a free 14-day trial for organizations interested in trying out the service.
Yes. OmniDefend MFA supports mobile devices, including both iOS and Android.
Yes. OmniDefend MFA provides an API for integrating with third-party applications and services.
